Compliance
SOC 2 Type I and II, SOC 1, and HIPAA audits for SaaS and cloud-first companies—plus readiness assessments.
View SOC 2
Trusted SOC 2 & HIPAA Audit Firm for SaaS and Cloud-First Companies
SOC 2 & HIPAA Audits in 4 Weeks, Guaranteed.
Companies that trust Zero Day
What We Do
SOC 2, SOC 1, and HIPAA audits for startups and growing companies on AWS, Azure, and Google Cloud.
SOC 2 Type I and II, SOC 1, and HIPAA audits for SaaS and cloud-first companies—plus readiness assessments.
View SOC 2Penetration testing, HIPAA risk analysis, and control reviews that strengthen your security before the audit.
View All Cybersecurity ServicesPolicies, vendor risk, and vCISO support—a long-term compliance partner, not just an auditor.
View All Business Support ServicesSchedule a consultation with our team and we'll help you determine whether SOC 2, HIPAA—or a combination—is right for your business, industry, and growth stage. Get clear guidance, defined next steps, and a compliance plan tailored to your goals.
Book Your FREE Consultation NowWho We Serve
SaaS, healthcare, fintech, AI, startups, logistics, and MSPs—scoped to how you operate.
We specialize in working with SaaS platforms hosted in cloud-native environments. SOC 2 is a baseline requirement for procurement and trust.
HIPAA and SOC 2 audits for digital health platforms and vendors handling PHI under BAAs.
SOC 2 and security control audits for fintech, regtech, and payments companies handling sensitive data or investor oversight.
SOC 2 support for MSPs offering DevOps, infrastructure, or security services to regulated clients.
SOC 2 for AI platforms handling customer data, model access, and cloud infrastructure.
First-time SOC 2 audits scoped to your team, product, and enterprise buyers.
SOC 2 for shipment, warehouse, and supply-chain platforms; SOC 1 where financial reporting is affected.
Built on Trust. Proven by Results.
Fast, fixed-fee SOC 2 and HIPAA audits with a 5-star client rating.
Independent reports that follow AICPA standards, trusted by regulators, investors, and enterprise buyers.
SOC 2, SOC 1, HIPAA, and pen testing without the busywork.
Methods built for cloud infrastructure.
Drata, Secureframe, Vanta, TrustCloud, and Sprinto.
Fixed fees from kickoff to final report.
CPA-issued reports in time for your deadlines.
Clients cite our responsiveness and clarity.
SOC 1, SOC 2, and HIPAA—made achievable.
CPA-led SOC 1, SOC 2, and HIPAA reporting.
Whether you're pursuing your first SOC 2 readiness assessment or renewing your reports, ZeroDay provides the expertise and structure needed to scale compliance alongside your business.
Evidence pulled straight from your cloud stack and GRC platform.
Risks stay visible without slowing your team.
Controls, policies, and evidence aligned before fieldwork—no surprises.
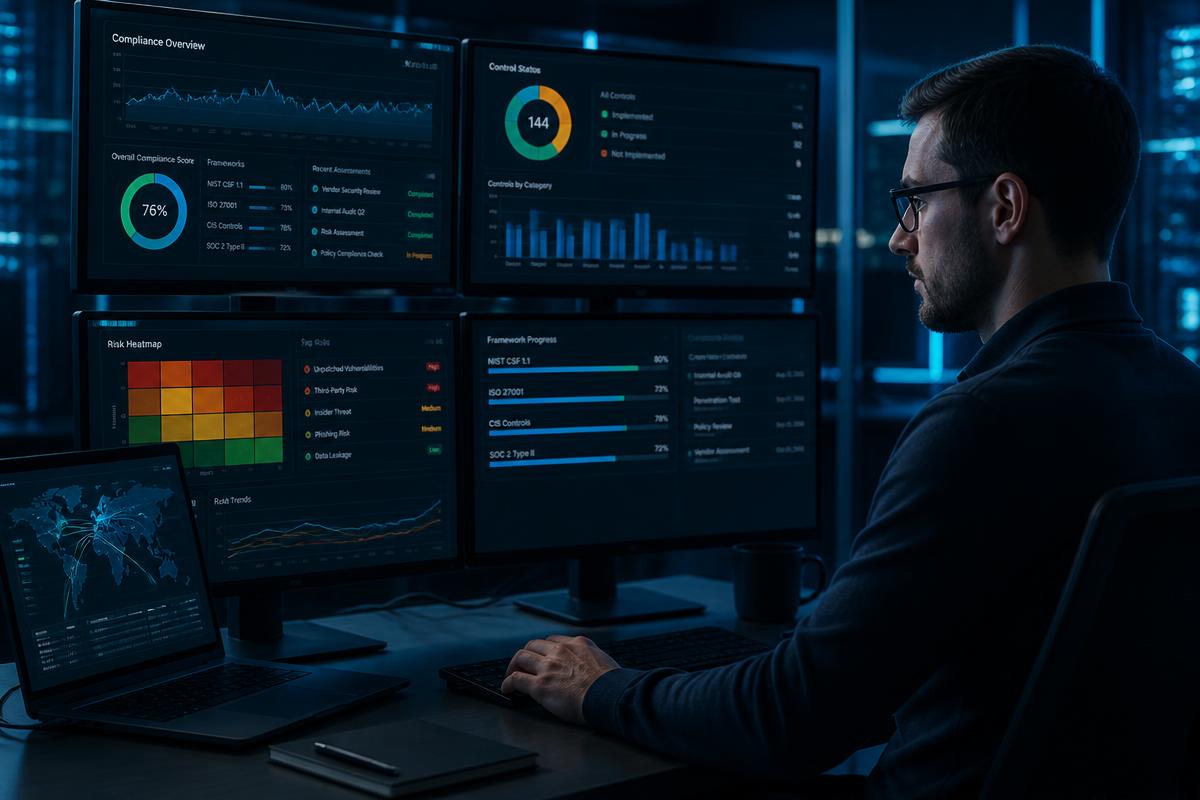
Seamless Integration
Drata, Vanta, Secureframe, TrustCloud, and Sprinto.
AWS, Azure, and Google Cloud.
Use the systems you already have.
Fast audits. Clear guidance. Real results.
Responsive, predictable, and on time.
“Patrick explained the process clearly and kept us on track. The report was delivered on time, exactly as promised.”
“Zero Day gave us confidence throughout the SOC 2 process. The audit was fast, smooth, and collaborative.”
“By far the most responsive audit team we've worked with. They understand startups and move fast.”
Automated, connected, and audit-ready.
We audit inside the GRC platform you already use.
Fill out the form to schedule a free, 30-minute consultation with a senior-level compliance expert today!
Why Work with Us: